Removing pay-as-you-go requirements for Edge for Business DLP unmanaged app protections

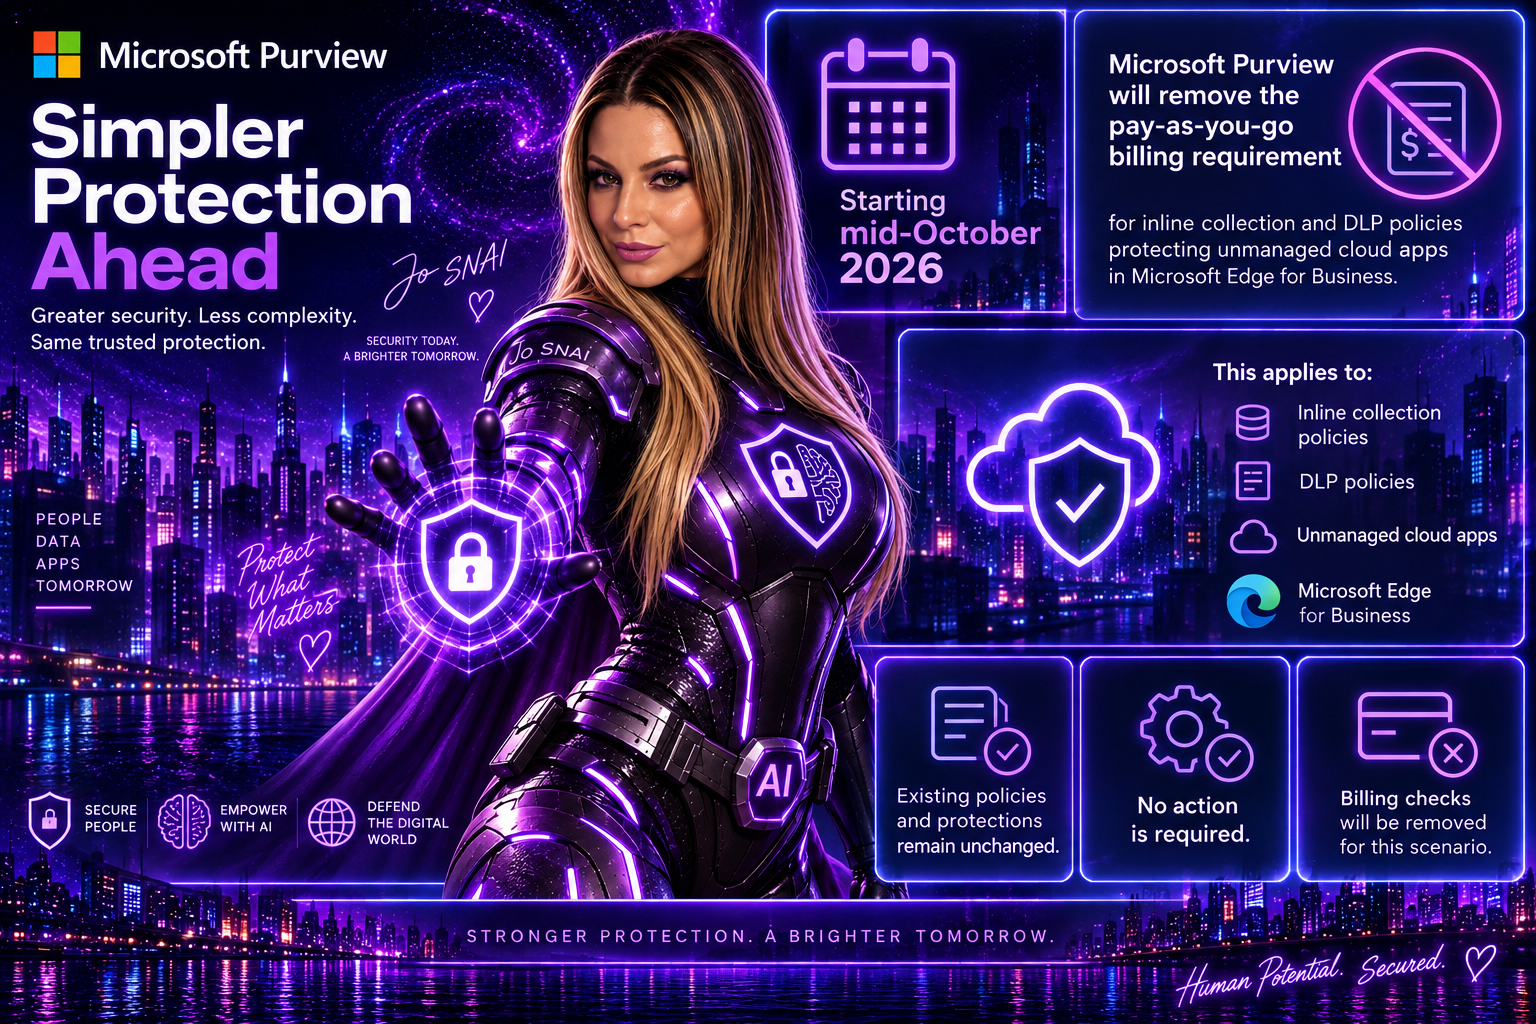
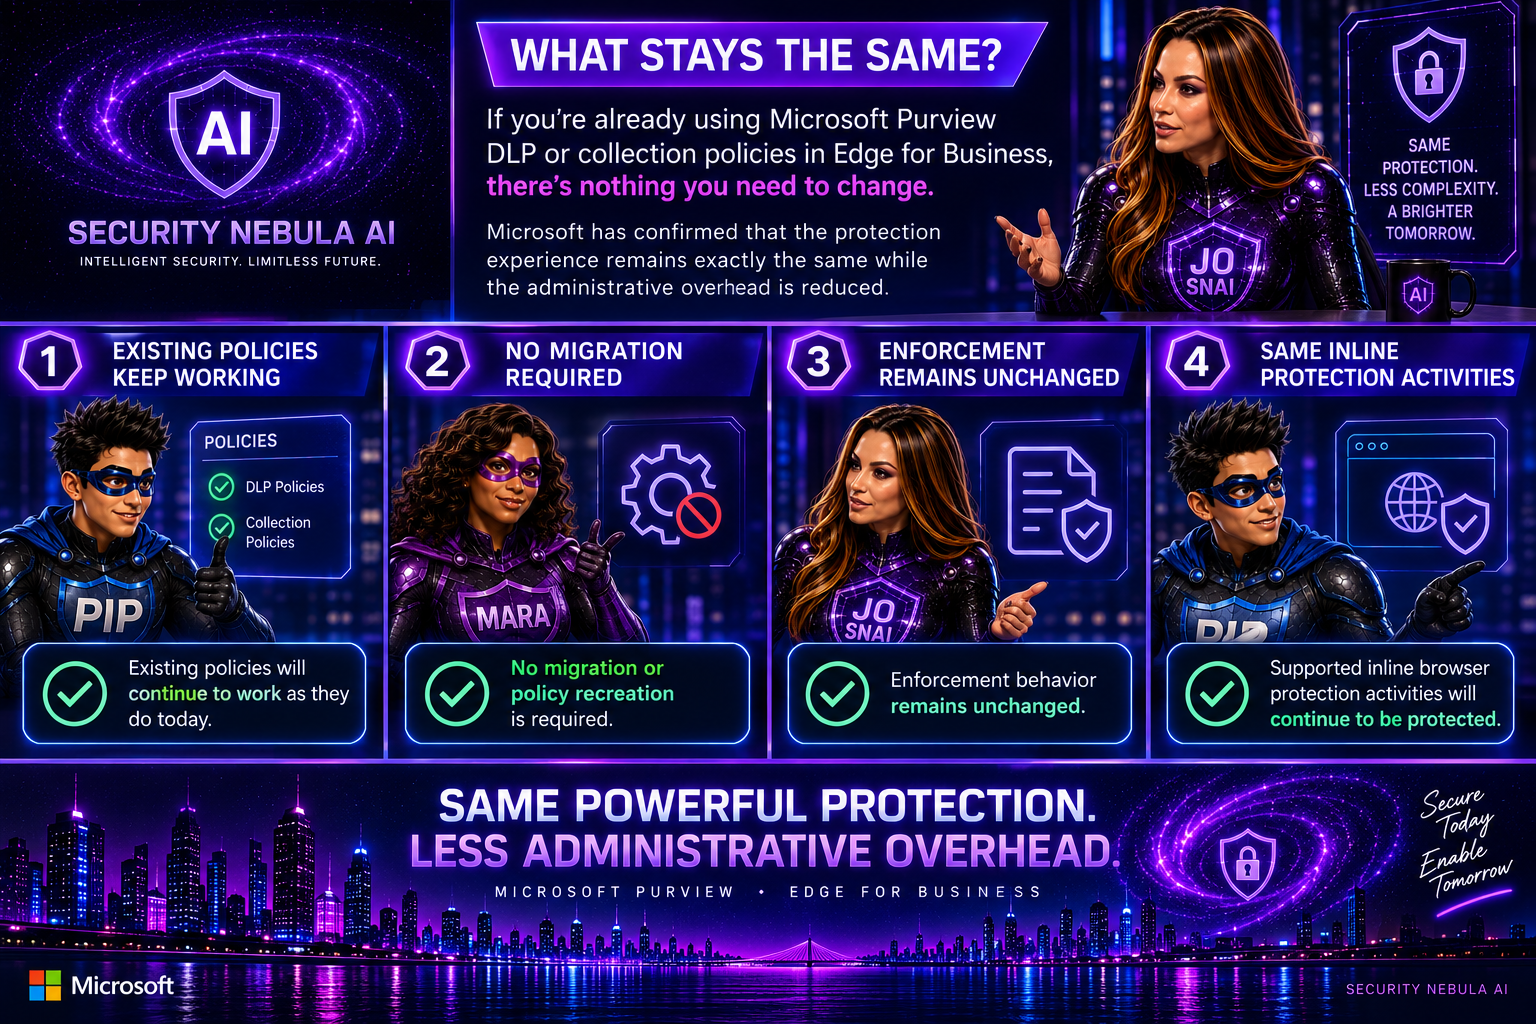
Good news for Microsoft Purview administrators. Microsoft is removing the pay-as-you-go (PAYG) billing requirement for Data Loss Prevention (DLP) and collection policies that protect unmanaged cloud app interactions in Microsoft Edge for Business. This change, rolling out starting in mid-October 2026, simplifies deployment and management by eliminating the need to connect an Azure subscription specifically for this Edge for Business protection scenario.
 

What’s Changing?

Until now, organizations that wanted to use Microsoft Purview’s inline protection capabilities for unmanaged cloud apps in Edge for Business needed to configure pay-as-you-go billing. Microsoft previously announced this requirement, but it has now decided to remove it.

Once the rollout is complete, administrators will no longer need:

  • An Azure subscription for this specific protection scenario
  • Pay-as-you-go billing configuration
  • Billing prerequisite validation checks when creating or editing applicable policies

The actual protection capabilities are not changing. This is purely a licensing and billing simplification.
 

What Stays the Same?

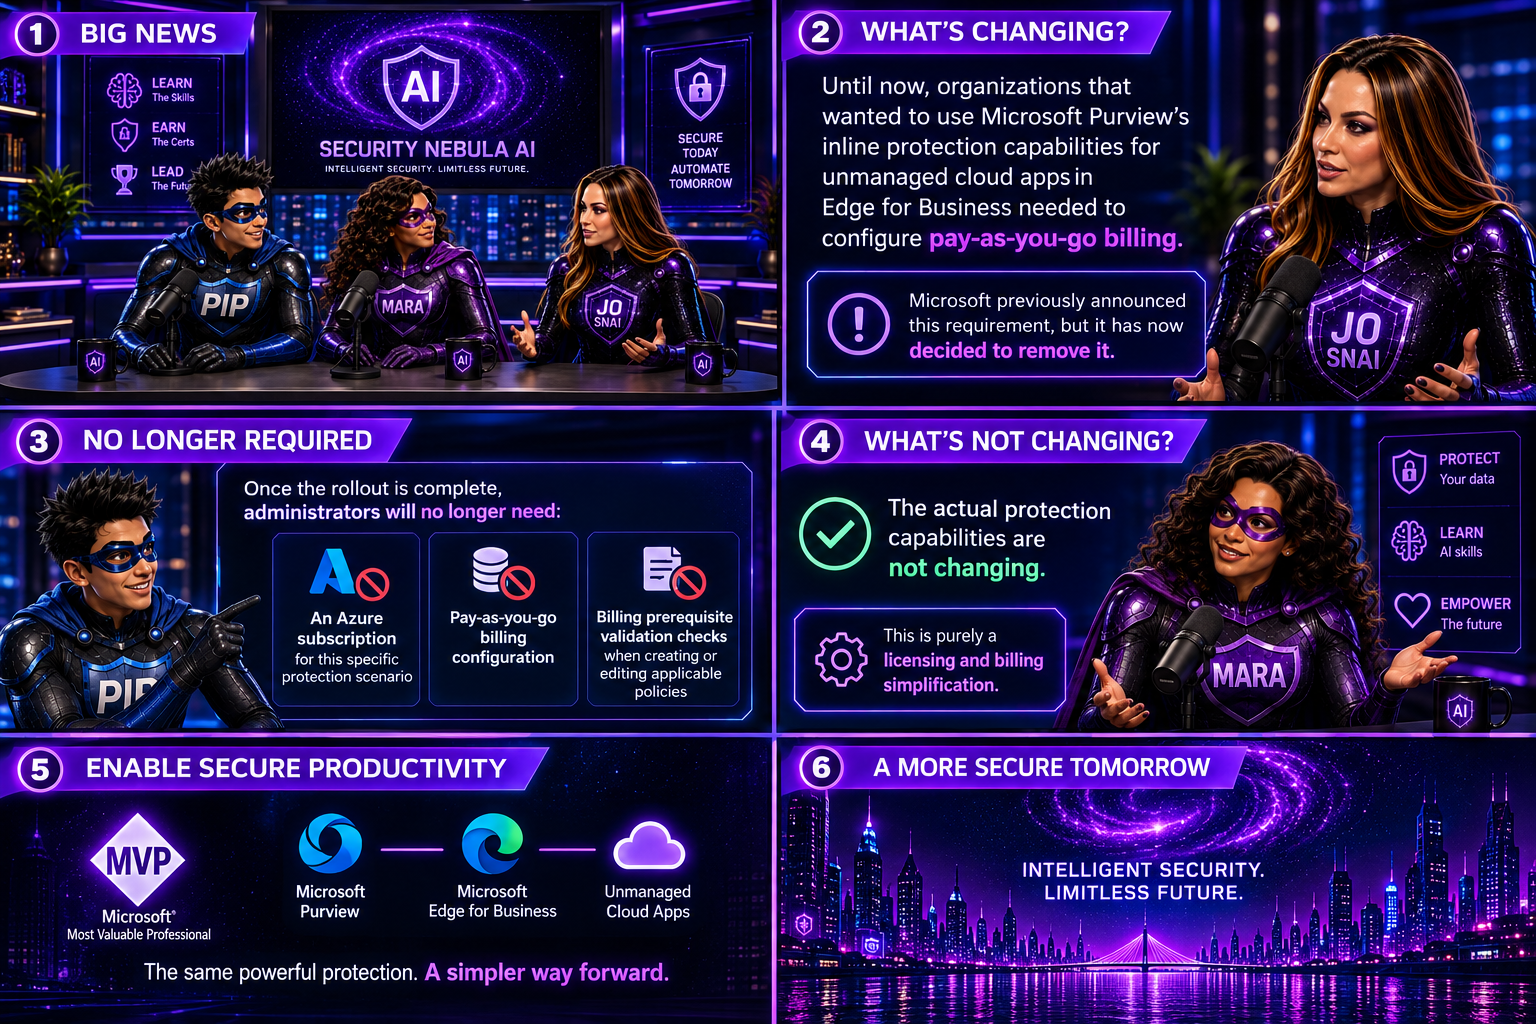
If you’re already using Purview DLP or collection policies in Edge for Business, there’s nothing you need to change.

Microsoft has confirmed that:

  • Existing policies will continue to work as they do today
  • No migration or policy recreation is required
  • Enforcement behavior remains unchanged
  • Supported inline browser protection activities will continue to be protected

In other words, the protection experience remains exactly the same while the administrative overhead is reduced.
 

Billing Impact

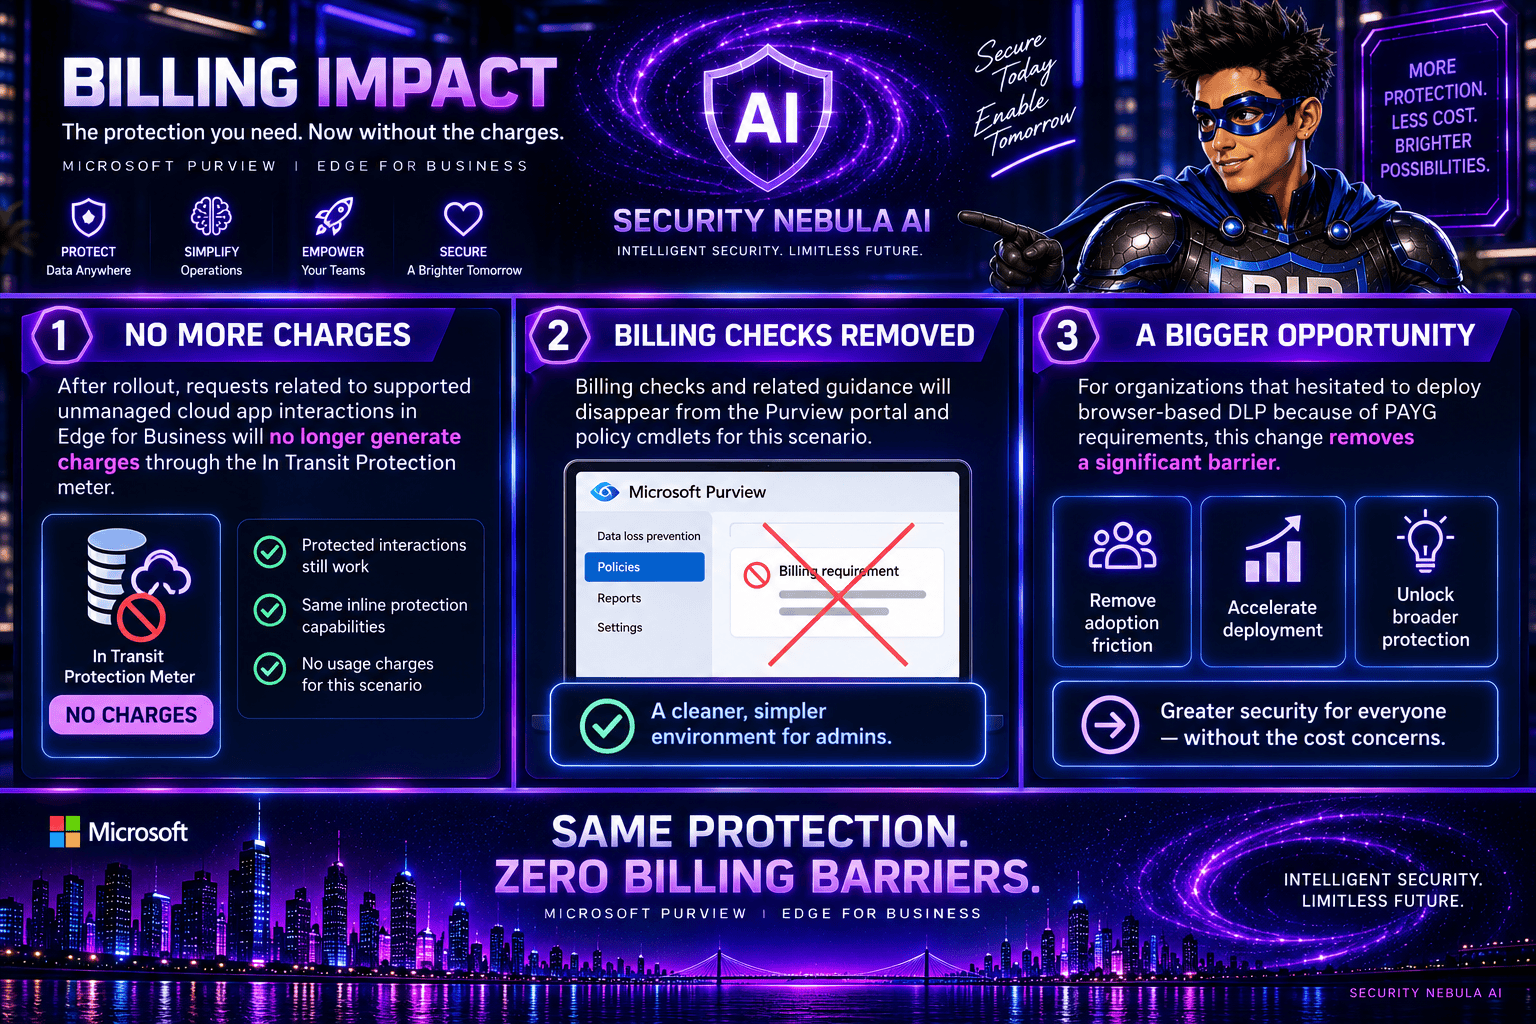
One of the biggest benefits of this update is the removal of charges associated with these protected interactions.

After rollout:

  • Requests related to supported unmanaged cloud app interactions in Edge for Business will no longer generate charges through the In Transit Protection meter.
  • Billing checks and related guidance will disappear from the Purview portal and policy cmdlets for this scenario.

For organizations that hesitated to deploy browser-based DLP because of PAYG requirements, this change removes a significant barrier.
 

Important: This Doesn’t Apply to Everything

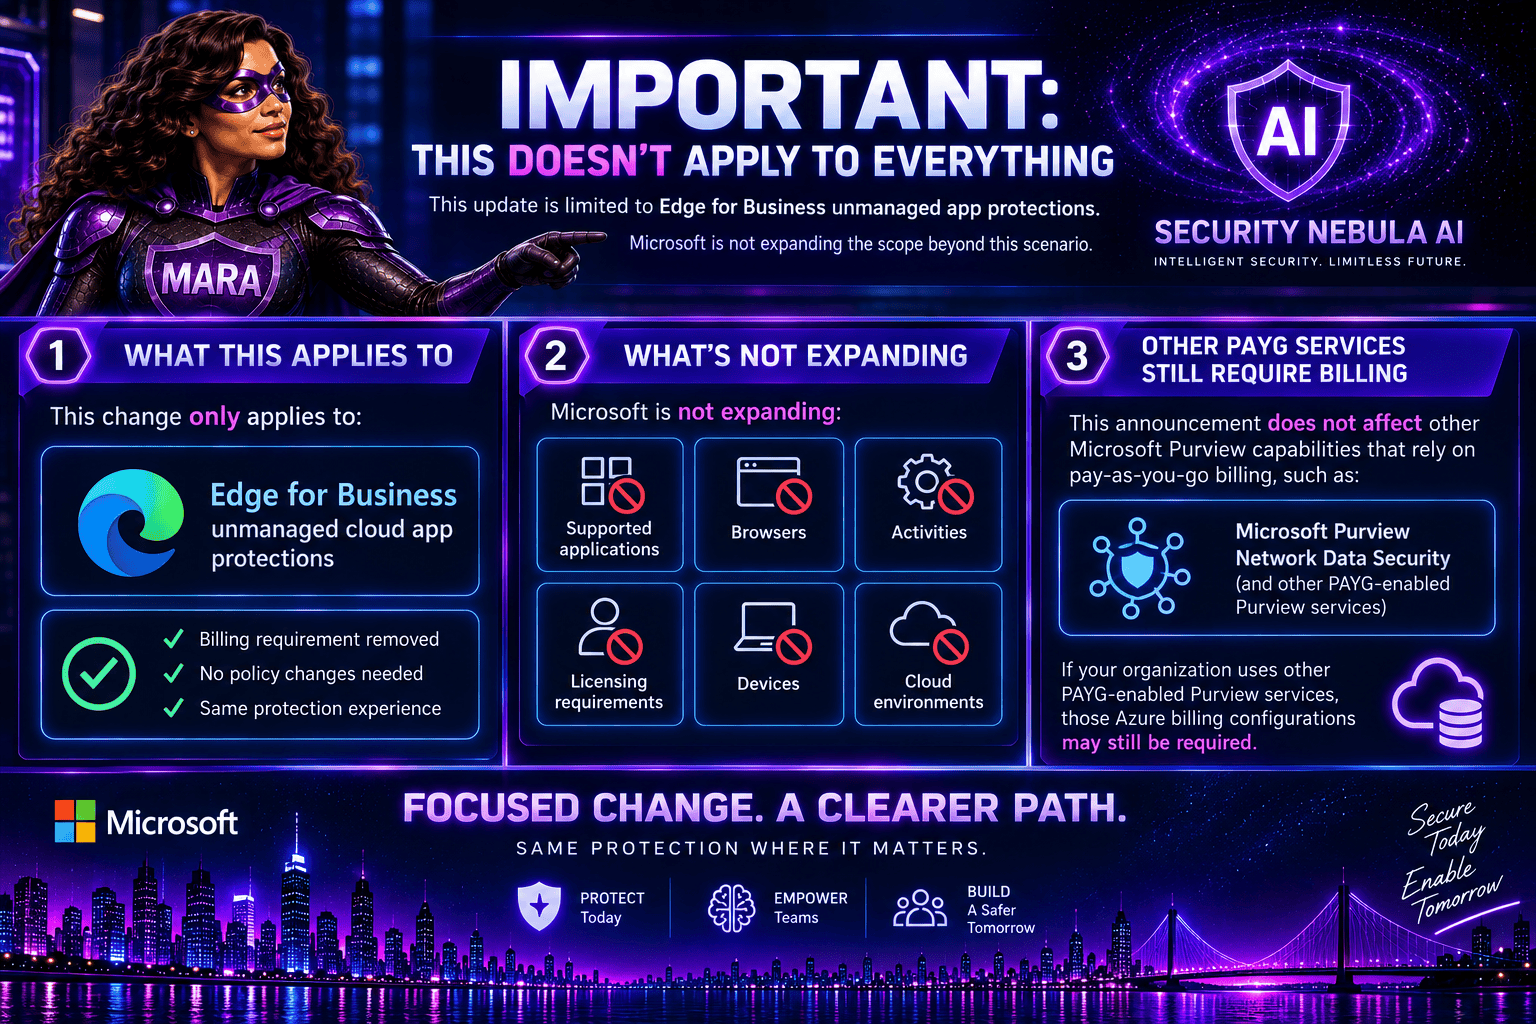
It’s worth noting that this update is limited to Edge for Business unmanaged app protections.

Microsoft is not expanding:

  • Supported applications
  • Browsers
  • Activities
  • Licensing requirements
  • Devices
  • Cloud environments

Additionally, other Microsoft Purview capabilities that rely on pay-as-you-go billing, such as Microsoft Purview Network Data Security, are not affected by this announcement. If your organization uses other PAYG-enabled Purview services, those Azure billing configurations may still be required.
 

Rollout Timeline

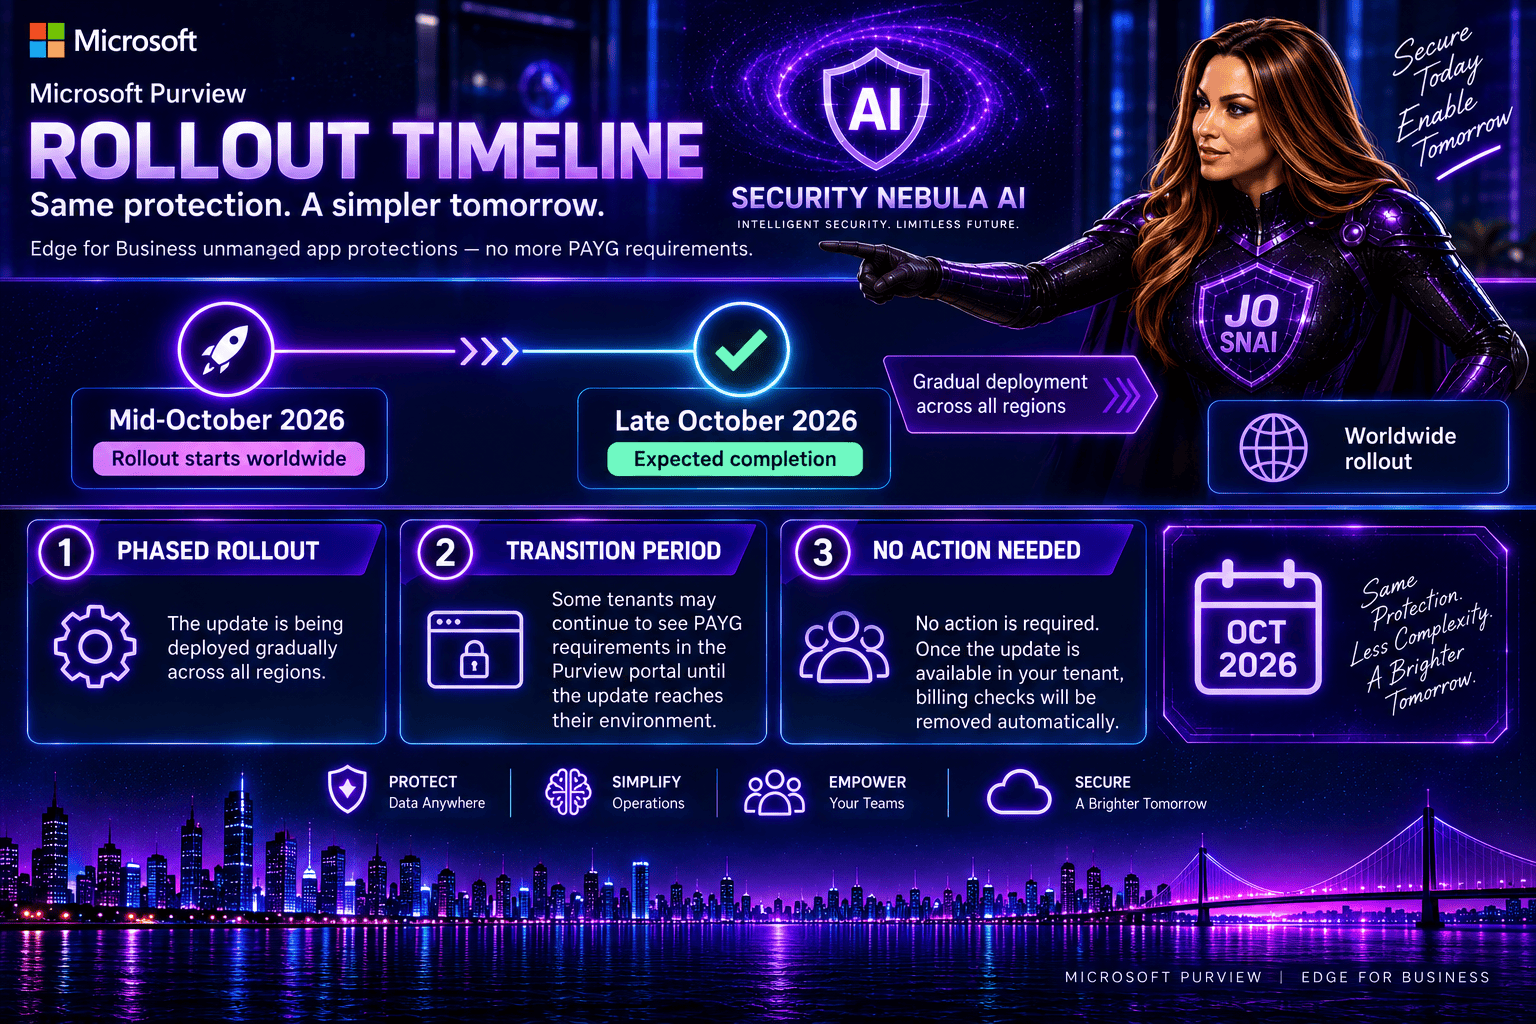
The update is scheduled to roll out worldwide:

  • Start: Mid-October 2026
  • Expected completion: Late October 2026

Because the deployment is gradual, some tenants may continue to see PAYG requirements in the Purview portal until the update reaches their environment.
 

What Should Administrators Do?

The short answer: nothing.

Microsoft has stated that no action is required.

However, I recommend administrators:

  1. Continue using existing DLP and collection policies as configured.
  2. Avoid removing Azure billing configurations that support other PAYG-based Purview workloads.
  3. Monitor Microsoft documentation during the rollout for updated guidance.
 

This is a welcome change that makes Microsoft Purview easier to adopt and manage. Security teams can continue protecting sensitive data flowing to unmanaged cloud applications through Edge for Business without having to worry about additional billing configuration or consumption-based charges for this use case.

While the underlying DLP capabilities remain unchanged, reducing administrative complexity is always a step in the right direction. For organizations looking to strengthen browser-based data protection, this removes one more obstacle and makes deployment a little more straightforward.
 

Microsoft Purview Adds Time-Limited Role Assignments to Strengthen Security

Microsoft is enhancing Microsoft Purview with a new capability that allows administrators to assign expiration dates to role group memberships. This update makes it easier to grant temporary administrative access while supporting the principle of least privilege, helping organizations reduce the risk associated with long-term privileged accounts.

With this new feature, administrators can specify how long a user or security group should remain in a Purview role group, choosing a duration anywhere from one day up to two years. Once the assigned period expires, access is automatically removed, helping security and compliance teams maintain tighter control over administrative permissions.

When Will It Be Available?

Microsoft plans to roll out the feature according to the following schedule:

  • Worldwide General Availability: Starting in late July 2026 and expected to complete by late August 2026.
  • GCC, GCC High, and DoD: Starting in late August 2026 and expected to complete by late September 2026.
What Does This Mean for Organizations?

This enhancement primarily benefits:

  • Microsoft Purview administrators
  • Security administrators
  • Compliance teams
  • Organizations managing role-based access through Microsoft Purview

The feature will be available through:

  • Microsoft Purview Compliance Portal
  • Microsoft Purview Role-Based Access Control (RBAC)
Key Benefits

Once the rollout is complete, administrators will be able to:

âś… Assign users or security groups to role groups with a predefined expiration date.

âś… Set assignment durations ranging from 1 day to 2 years.

âś… Apply the capability to both new and existing role assignments.

âś… Reduce the likelihood of forgotten or unnecessary privileged access.

âś… Improve governance, compliance, and security posture with minimal administrative effort.

Importantly, existing role assignments will not be automatically modified, and end-user workflows will remain unchanged.

What Do You Need to Do?

The good news is that no action is required to enable this feature. It will be available by default once deployed, with no additional configuration or policy changes needed.

However, organizations may want to take advantage of the new functionality by:

  • Reviewing privileged access management processes.
  • Using expiration-based assignments for temporary projects, audits, or administrative tasks.
  • Updating internal documentation and operational procedures.
  • Informing Purview administrators about the new capability.

From a compliance perspective, time-limited role assignments help organizations demonstrate stronger control over privileged access.

Many regulatory frameworks and security standards—including ISO 27001, NIST, SOC 2, GDPR accountability requirements, and Zero Trust security principles—expect organizations to follow the principle of least privilege, ensuring users only have access to the resources they need and only for as long as they need it.

🚀 Strengthening Security in Microsoft Purview & Microsoft 365: Important Update Coming Soon

To further enhance the security and integrity of how Microsoft Purview interacts with Microsoft 365 services—such as Exchange, SharePoint, OneDrive, and Teams—Microsoft is modernizing how role management works within Purview.

Beginning mid‑February through late March 2026, Microsoft Purview will automatically map certain high‑privileged Purview admin roles to three newly created Microsoft Entra roles. This alignment strengthens identity and permission boundaries and ensures that all high‑impact actions (like search or export) are performed only by users with validated permissions in Entra.

đź“… Rollout Timeline

General Availability (Worldwide)
⏳ Begins: Mid‑February 2026
⏳ Complete: Late March 2026

The best part? No customer action is required.

Role assignments will synchronize automatically from Purview to Entra within minutes, ensuring that permissions flow securely and consistently across Microsoft 365.

📝 How to Prepare

  • No action is required—synchronization is fully automated.
  • Be aware that new Purview‑specific Entra roles may appear in audit logs.
  • Avoid assigning these roles directly in Entra.
  • Review your internal documentation and update governance workflows if needed.
  • For deeper technical detail, refer to Microsoft Purview documentation.

🏢 Impact on Your Environment

âś” Who Is Affected

Organizations with admins assigned to high‑privileged Purview roles.

✔ What You’ll See

  • New Purview‑specific Entra roles appearing in audit logs
  • Auto‑generated Entra role assignments, managed solely by Purview
  • No disruption to existing workflows or permissions

âś” What You Need To Do

  • No action required
  • DO NOT manually assign these roles in Entra
  • Update documentation or internal governance policies if referencing these roles
  • Inform your security/compliance teams about the new audit log entries

Compliance & Security Notes

  • No new compliance concerns identified
  • Mapping ensures consistent identity + permission enforcement across M365
  • Supports least‑privileged access by validating roles in both Purview and Entra