Microsoft Purview Tightens Rules for Custom Sensitive Information Types

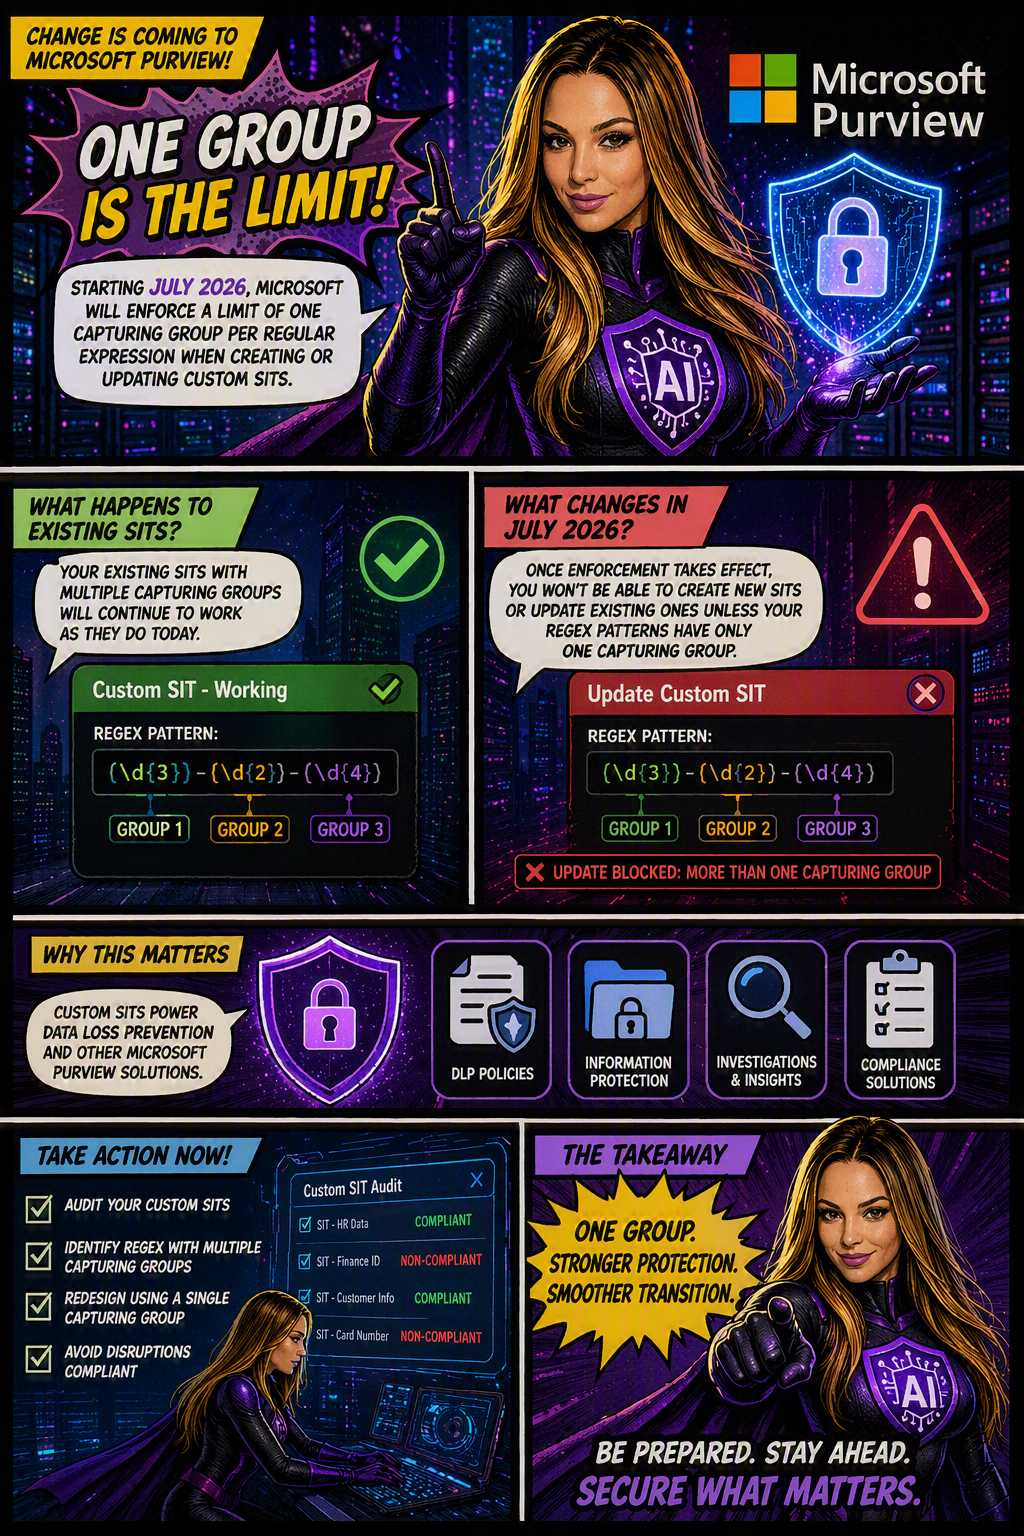
Organizations using Microsoft Purview custom Sensitive Information Types (SITs) should be aware of an upcoming change that may require updates to existing regex patterns.

Microsoft is moving forward with enforcing a long-documented rule that allows only one capturing group per regular expression in custom SIT definitions. The goal is to improve the consistency, reliability, and predictability of how sensitive data is identified and classified across Microsoft Purview and Data Loss Prevention (DLP) workloads.

When is this happening?

The rollout is expected to be completed by early July 2026 across all Microsoft cloud environments, including:

  • Worldwide
  • GCC
  • GCC High
  • DoD
Who is affected?

This change primarily impacts:

  • Microsoft Purview administrators
  • Compliance teams managing custom Sensitive Information Types
  • Organizations using custom SITs in DLP, data classification, and compliance solutions

The enforcement applies whether SITs are managed through:

  • The Microsoft Purview portal
  • PowerShell, including:
    • New-DlpSensitiveInformationTypeRulePackage
    • Set-DlpSensitiveInformationTypeRulePackage
What changes?

Once enforcement is in place:

✅ New custom SITs must contain only one capturing group in each regular expression.

❌ Creating a new SIT with multiple capturing groups will be blocked.

❌ Updating an existing SIT that contains multiple capturing groups will fail validation.

❌ Administrators will not be able to save changes to existing SITs until non-compliant regex patterns are updated.

What about existing SITs?

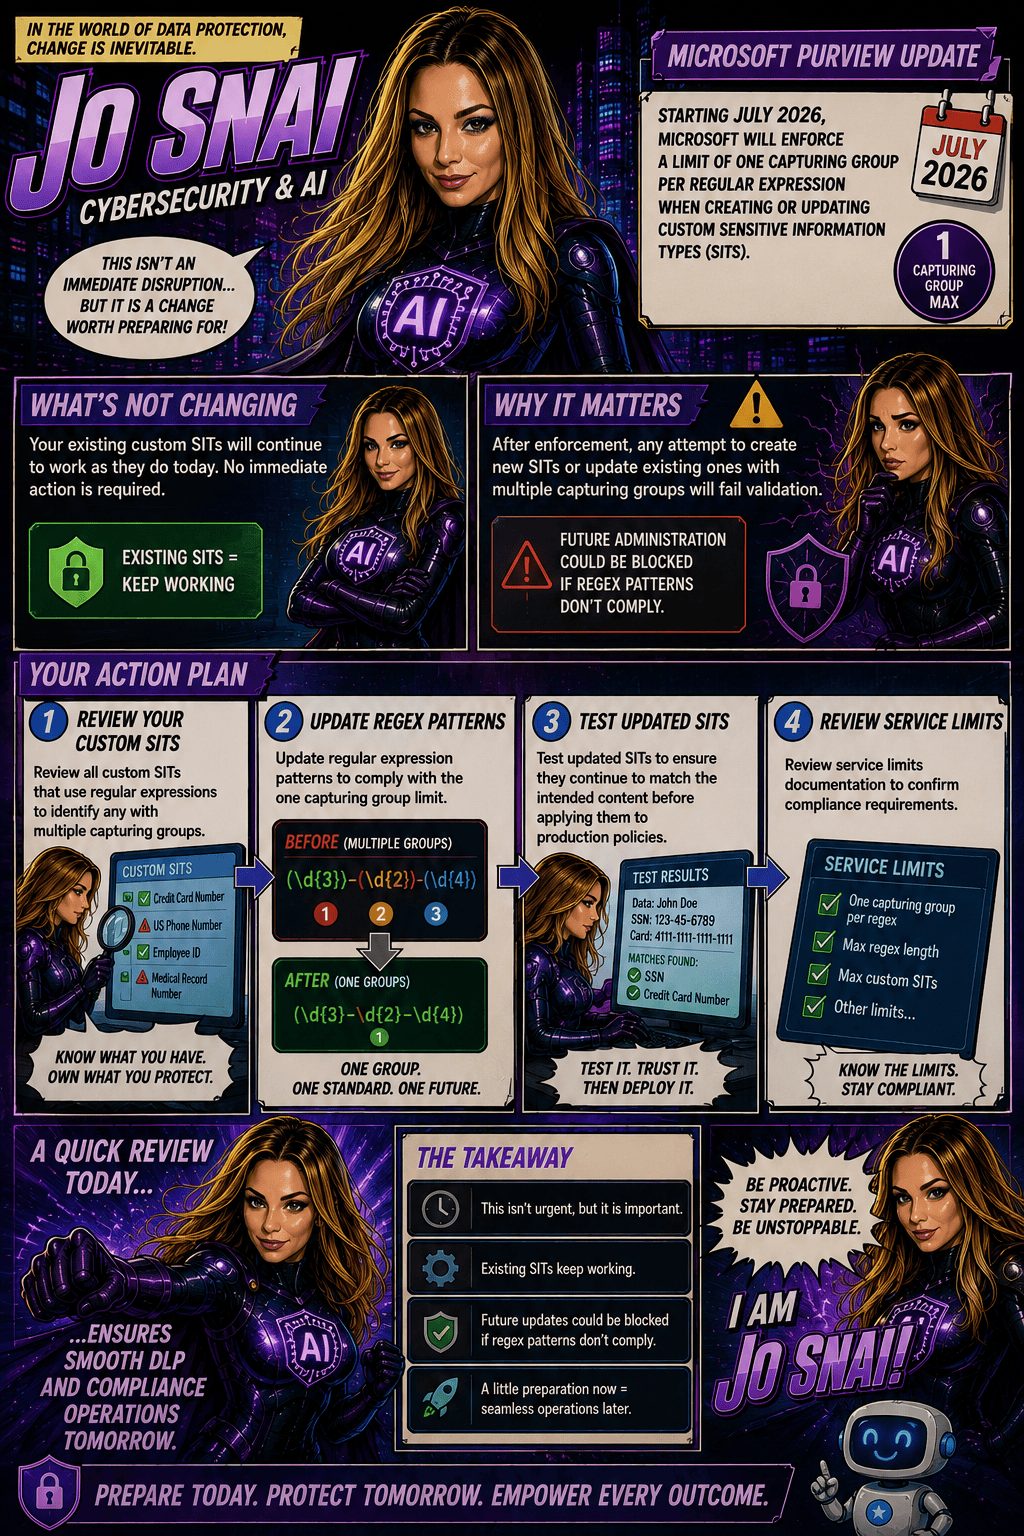
Existing custom SITs that contain multiple capturing groups will continue to work in their current state. However, they become a potential issue the moment you need to modify, update, or re-save them.

In other words, if an existing SIT contains a regex pattern with multiple capturing groups, you’ll need to redesign that pattern to comply with the one-capturing-group rule before any future changes can be saved.

Many organizations rely on custom SITs to identify sensitive business information and power key compliance capabilities such as:

Why does this matter?
  • Data Loss Prevention (DLP)
  • Data classification
  • Compliance monitoring
  • Information protection policies

If a custom SIT cannot be updated because it fails validation, it could delay policy changes, compliance updates, or new data protection initiatives.
What should you do now?

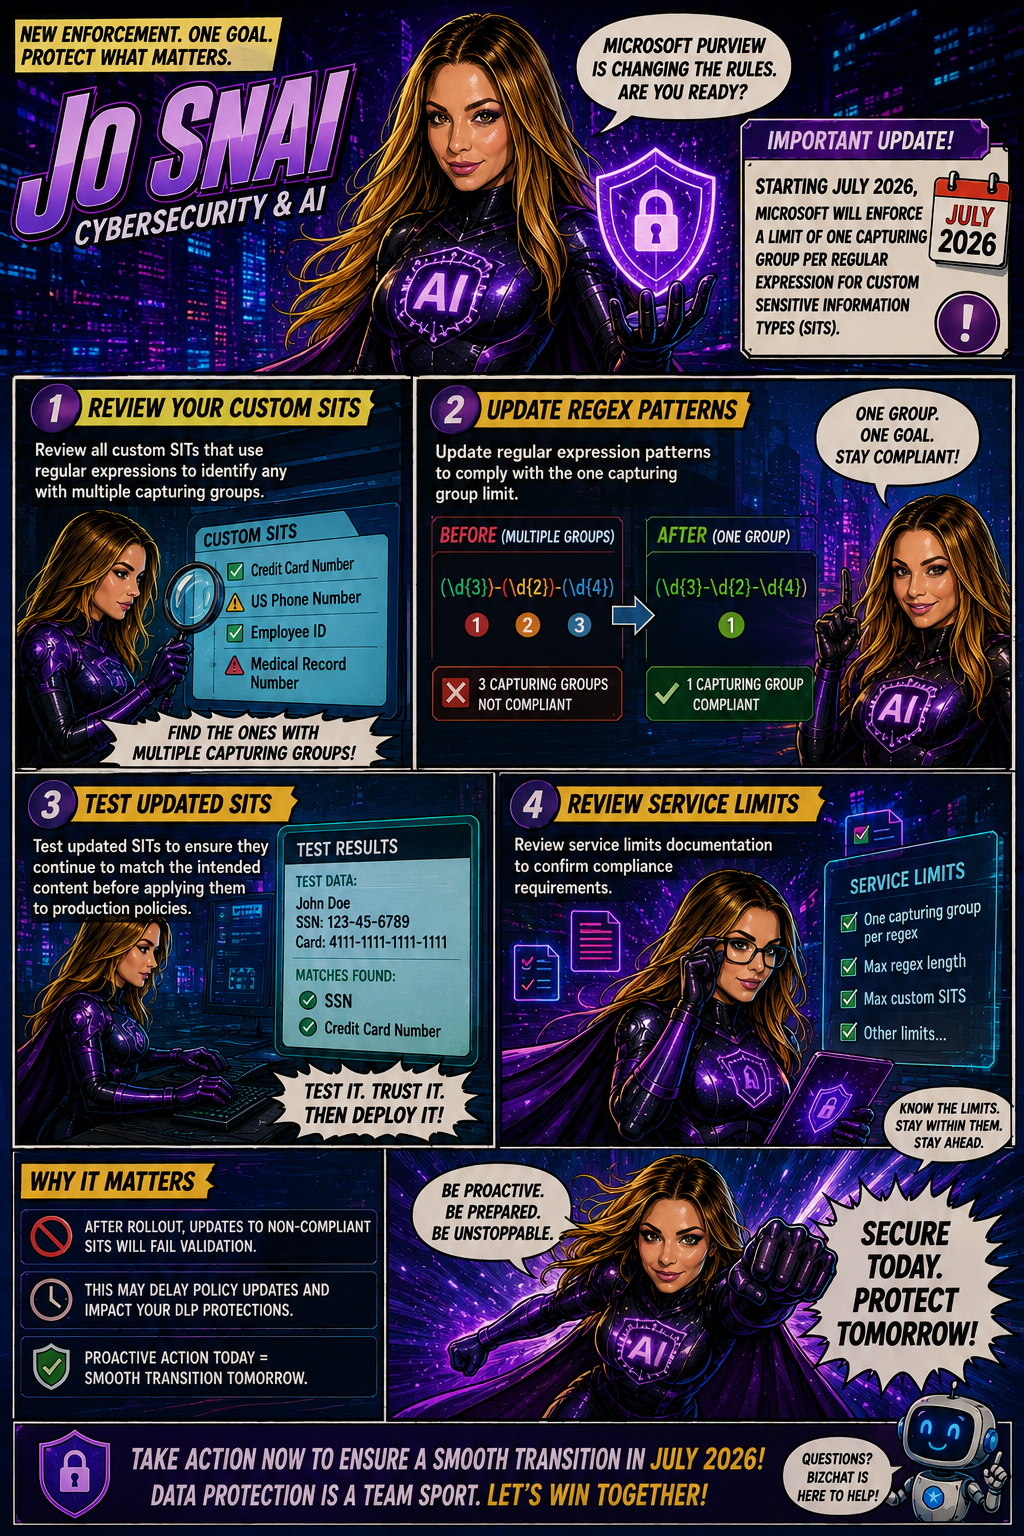
To avoid surprises, Microsoft Purview administrators should proactively:

  1. Audit existing custom SITs
  2. Identify regex patterns that use multiple capturing groups
  3. Redesign patterns to use a single capturing group
  4. Test and validate updated SITs before future modifications are required
Microsoft Purview Adds Time-Limited Role Assignments to Strengthen Security

Microsoft is enhancing Microsoft Purview with a new capability that allows administrators to assign expiration dates to role group memberships. This update makes it easier to grant temporary administrative access while supporting the principle of least privilege, helping organizations reduce the risk associated with long-term privileged accounts.

With this new feature, administrators can specify how long a user or security group should remain in a Purview role group, choosing a duration anywhere from one day up to two years. Once the assigned period expires, access is automatically removed, helping security and compliance teams maintain tighter control over administrative permissions.

When Will It Be Available?

Microsoft plans to roll out the feature according to the following schedule:

  • Worldwide General Availability: Starting in late July 2026 and expected to complete by late August 2026.
  • GCC, GCC High, and DoD: Starting in late August 2026 and expected to complete by late September 2026.
What Does This Mean for Organizations?

This enhancement primarily benefits:

  • Microsoft Purview administrators
  • Security administrators
  • Compliance teams
  • Organizations managing role-based access through Microsoft Purview

The feature will be available through:

  • Microsoft Purview Compliance Portal
  • Microsoft Purview Role-Based Access Control (RBAC)
Key Benefits

Once the rollout is complete, administrators will be able to:

✅ Assign users or security groups to role groups with a predefined expiration date.

✅ Set assignment durations ranging from 1 day to 2 years.

✅ Apply the capability to both new and existing role assignments.

✅ Reduce the likelihood of forgotten or unnecessary privileged access.

✅ Improve governance, compliance, and security posture with minimal administrative effort.

Importantly, existing role assignments will not be automatically modified, and end-user workflows will remain unchanged.

What Do You Need to Do?

The good news is that no action is required to enable this feature. It will be available by default once deployed, with no additional configuration or policy changes needed.

However, organizations may want to take advantage of the new functionality by:

  • Reviewing privileged access management processes.
  • Using expiration-based assignments for temporary projects, audits, or administrative tasks.
  • Updating internal documentation and operational procedures.
  • Informing Purview administrators about the new capability.

From a compliance perspective, time-limited role assignments help organizations demonstrate stronger control over privileged access.

Many regulatory frameworks and security standards—including ISO 27001, NIST, SOC 2, GDPR accountability requirements, and Zero Trust security principles—expect organizations to follow the principle of least privilege, ensuring users only have access to the resources they need and only for as long as they need it.