💜🏆Honored to Be Renewed as a Microsoft MVP for a Second Year

Some milestones feel just as special the second time around.

I’m incredibly grateful and honored to share that I have been renewed as a Microsoft Most Valuable Professional (MVP) for another year in M365 Copilot and Microsoft Purview.

When I first received the MVP award, I saw it as both a recognition and a responsibility. A responsibility to continue learning, sharing knowledge, supporting the community, and helping others get the most value from Microsoft technologies.

Over the past year, the pace of innovation has been extraordinary. The rapid evolution of AI, the growing adoption of Microsoft 365 Copilot, and the increasing importance of data security, governance, and compliance through Microsoft Purview have made this an exciting time to contribute to the community.

As I reflect on the past year, I’m grateful for every opportunity to engage with fellow professionals, exchange ideas, share experiences, create content, and learn from some of the brightest minds in the Microsoft ecosystem. The MVP community is filled with individuals who are passionate about helping others succeed, and it is a privilege to be part of it.

This renewal is not just about individual achievements. It represents the value of collaboration, community, and continuous growth. Every conversation, challenge, lesson learned, and connection made along the way has contributed to this journey.

Thank you to Microsoft for this continued recognition and trust. Thank you to the MVP Program team, my colleagues, friends, mentors, customers, and the incredible community members who inspire me every day.

Most importantly, thank you to everyone who shares their knowledge, asks thoughtful questions, provides feedback, and helps make our community stronger. Your contributions are what make this ecosystem thrive.
As I begin my second year as an MVP, I’m excited to continue exploring what’s possible with AI, M365 Copilot, and Microsoft Purview, while giving back to the community that has given me so much.

Here’s to another year of learning, sharing, growing, and making an impact together.

Thank you for being part of the journey. 💜

Joanna Vathis
Microsoft MVP | M365 Copilot | Microsoft Purview
🎙️ New Broadcast Episode: Microsoft Purview Time-Limited Role Assignments

In this episode, we dive into the new Microsoft Purview Time-Limited Role Assignments feature, which allows administrators to grant temporary access to Purview role groups with automatic expiration.

Learn how this enhancement helps organizations implement least-privilege access, reduce privilege creep, strengthen governance, and improve compliance.

✅ Feature overview
✅ Security and compliance benefits
✅ Common use cases
✅ What admins need to know

🔔 Don’t forget to 👍 Like, ✅ Subscribe, and 🔔 Turn On Notifications for more Microsoft 365 ☁️, Security 🛡️, and Microsoft Purview 📋 updates! 🚀✨

🎙️ New Broadcast Episode: Microsoft Purview Time-Limited Role Assignments

Watch on YouTube ➡️

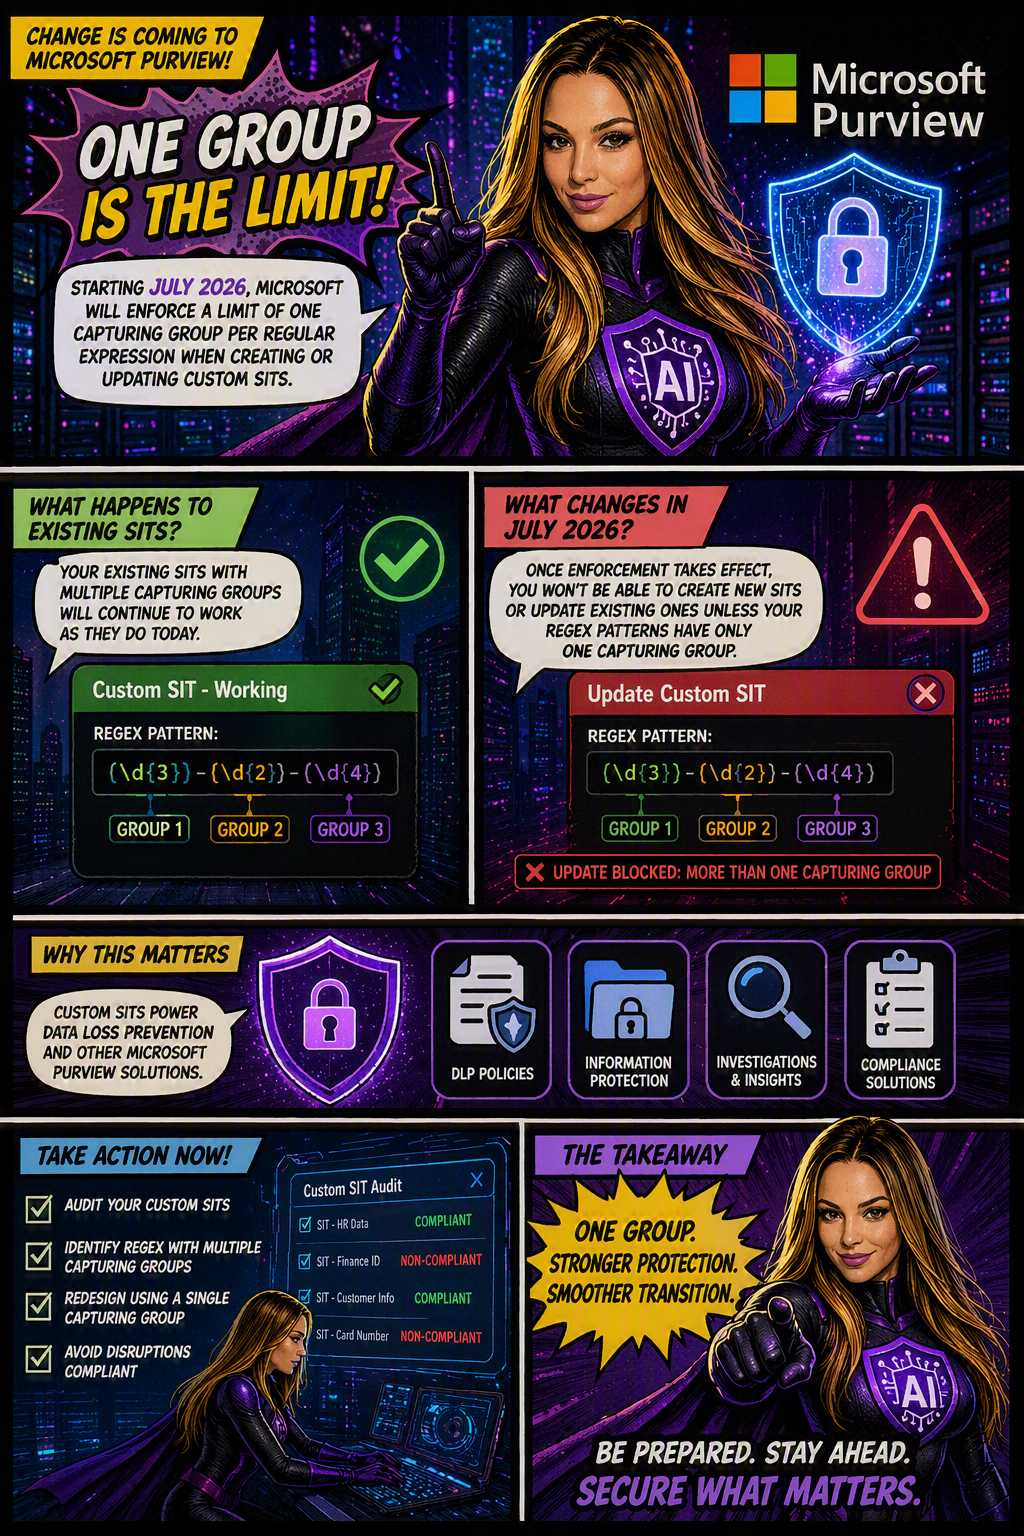
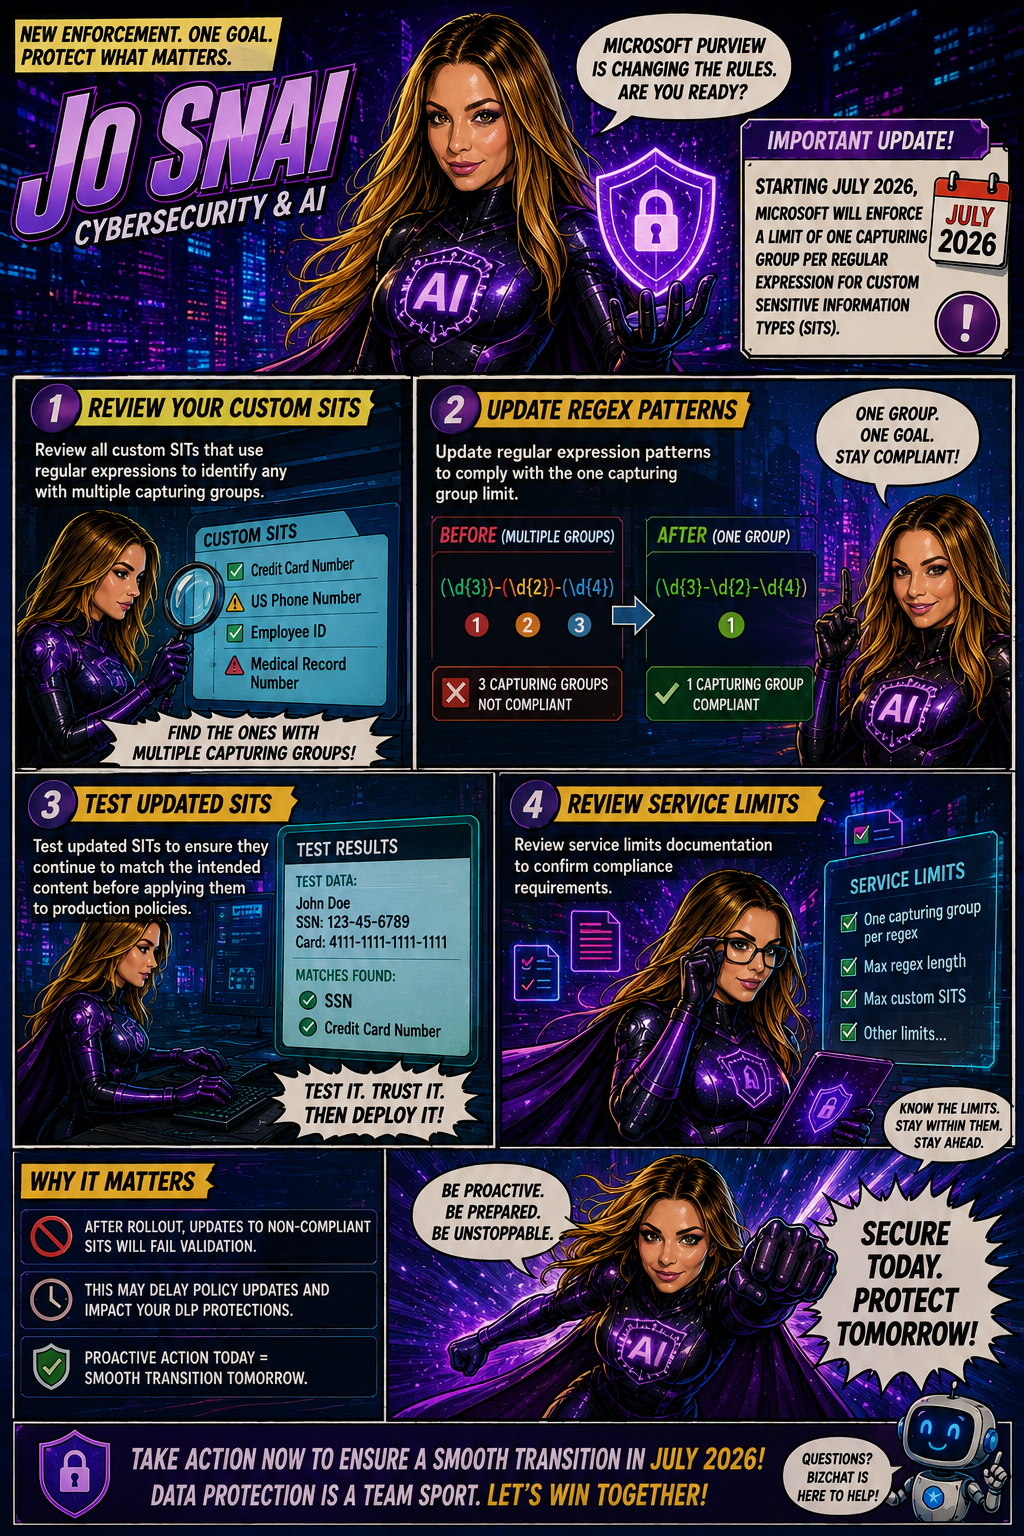
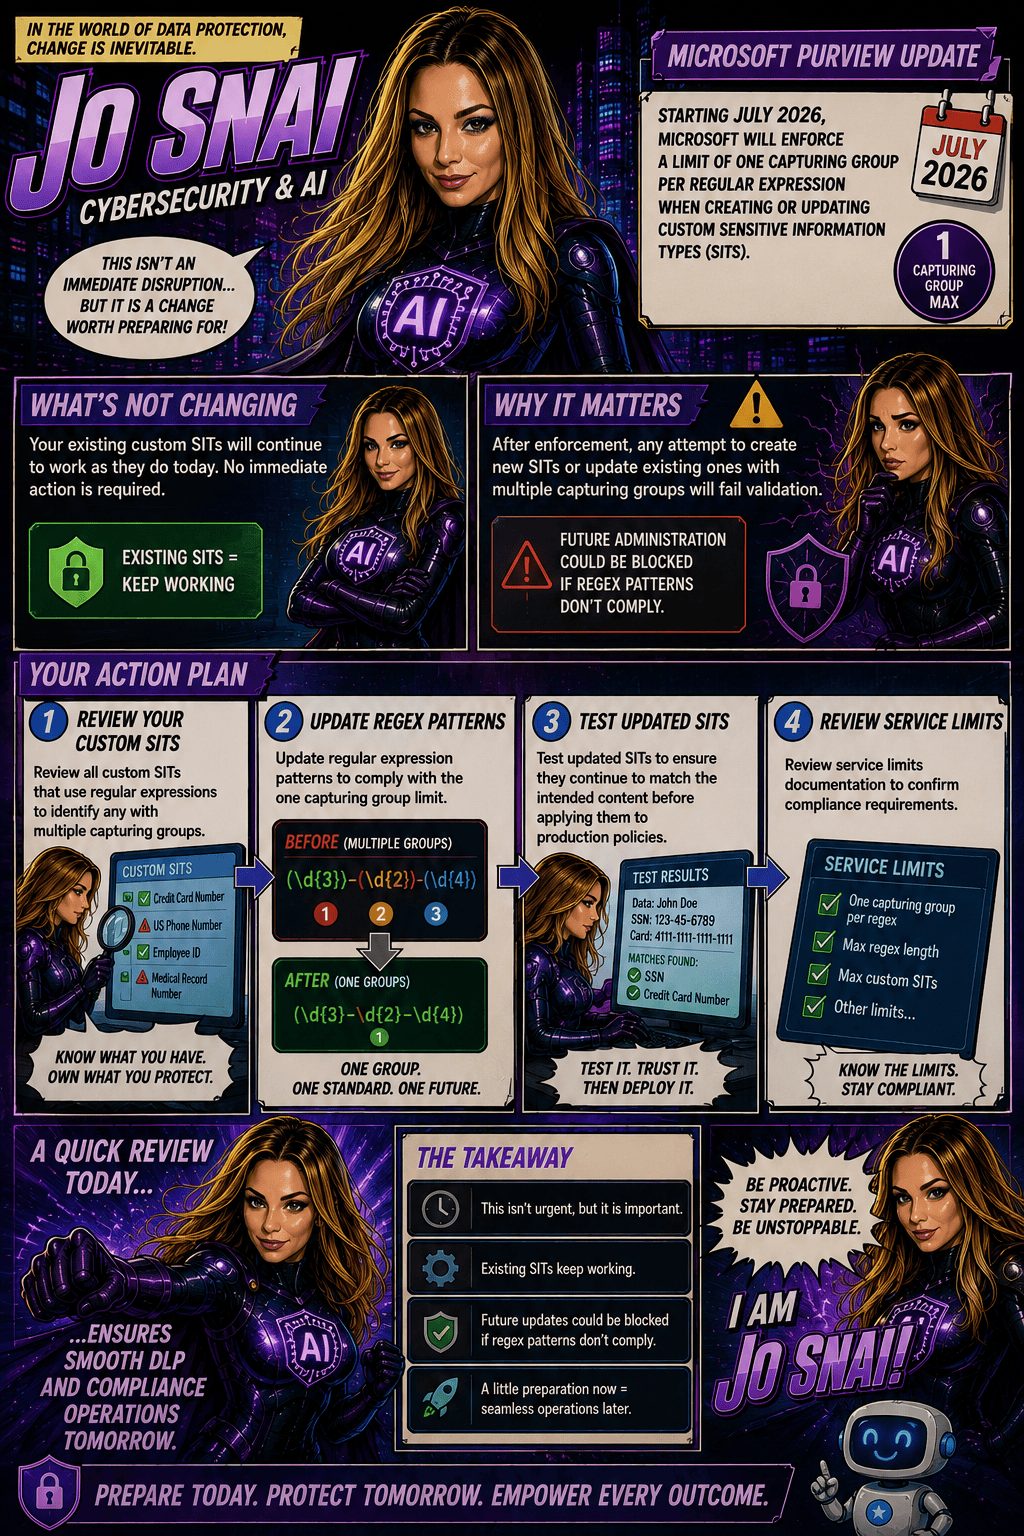
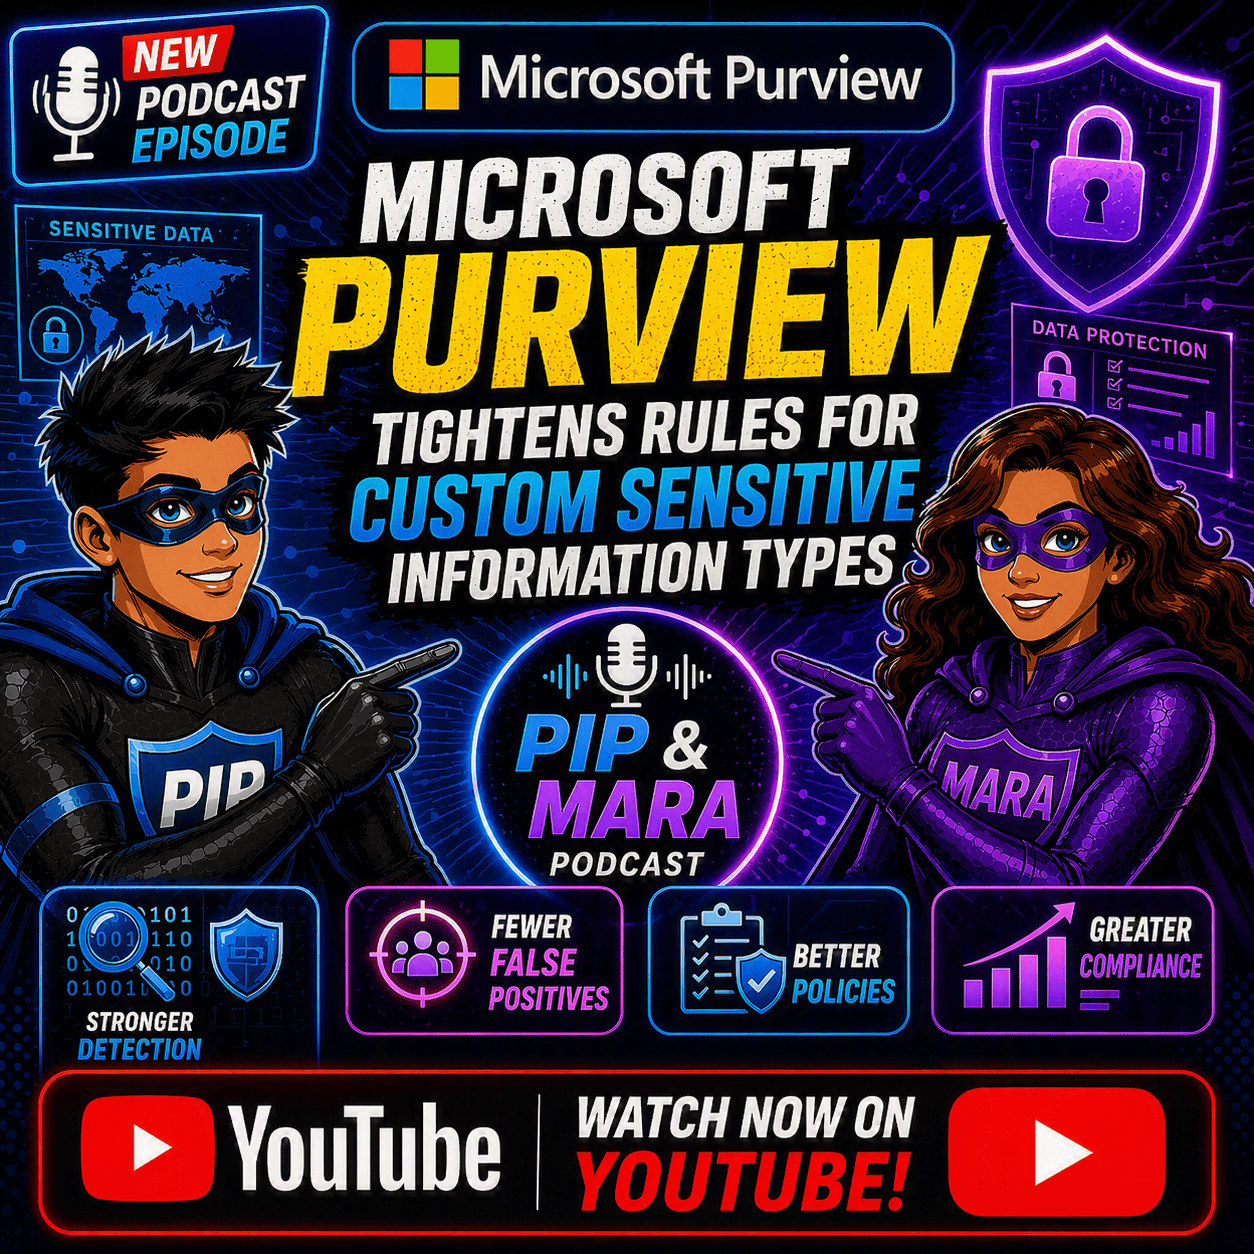
Microsoft Purview Tightens Rules for Custom Sensitive Information Types

Organizations using Microsoft Purview custom Sensitive Information Types (SITs) should be aware of an upcoming change that may require updates to existing regex patterns.

Microsoft is moving forward with enforcing a long-documented rule that allows only one capturing group per regular expression in custom SIT definitions. The goal is to improve the consistency, reliability, and predictability of how sensitive data is identified and classified across Microsoft Purview and Data Loss Prevention (DLP) workloads.

When is this happening?

The rollout is expected to be completed by early July 2026 across all Microsoft cloud environments, including:

  • Worldwide
  • GCC
  • GCC High
  • DoD
Who is affected?

This change primarily impacts:

  • Microsoft Purview administrators
  • Compliance teams managing custom Sensitive Information Types
  • Organizations using custom SITs in DLP, data classification, and compliance solutions

The enforcement applies whether SITs are managed through:

  • The Microsoft Purview portal
  • PowerShell, including:
    • New-DlpSensitiveInformationTypeRulePackage
    • Set-DlpSensitiveInformationTypeRulePackage
What changes?

Once enforcement is in place:

✅ New custom SITs must contain only one capturing group in each regular expression.

❌ Creating a new SIT with multiple capturing groups will be blocked.

❌ Updating an existing SIT that contains multiple capturing groups will fail validation.

❌ Administrators will not be able to save changes to existing SITs until non-compliant regex patterns are updated.

What about existing SITs?

Existing custom SITs that contain multiple capturing groups will continue to work in their current state. However, they become a potential issue the moment you need to modify, update, or re-save them.

In other words, if an existing SIT contains a regex pattern with multiple capturing groups, you’ll need to redesign that pattern to comply with the one-capturing-group rule before any future changes can be saved.

Many organizations rely on custom SITs to identify sensitive business information and power key compliance capabilities such as:

Why does this matter?
  • Data Loss Prevention (DLP)
  • Data classification
  • Compliance monitoring
  • Information protection policies

If a custom SIT cannot be updated because it fails validation, it could delay policy changes, compliance updates, or new data protection initiatives.

What should you do now?

To avoid surprises, Microsoft Purview administrators should proactively:

  1. Audit existing custom SITs
  2. Identify regex patterns that use multiple capturing groups
  3. Redesign patterns to use a single capturing group
  4. Test and validate updated SITs before future modifications are required

🛡️ Jo SNAI Reimagined: Same Mission. New Look. Bigger Impact.

Some characters evolve not because their purpose changes, but because the world around them does.

Since the beginning, Jo SNAI has represented the vision behind Security Nebula AI (SNAI), a place where cybersecurity, artificial intelligence, and innovation converge to create a safer and smarter digital future. As a digital superhero, Jo SNAI has always stood for protection, knowledge, resilience, and the responsible use of emerging technologies.

Today, Jo SNAI unveils a bold new look.

The transition from the original blue design to the new purple powered appearance, is more than a visual refresh. It reflects the growth of Security Nebula AI and the expanding role of AI in cybersecurity, automation, and digital transformation. The new design symbolizes innovation, creativity, intelligence, and the limitless possibilities that emerge when security and AI work together.

While the appearance has evolved, the mission remains unchanged.

Jo SNAI continues to champion the values that define Security Nebula AI: protecting what matters most, empowering people through technology, embracing innovation responsibly, and helping organizations navigate the future with confidence.

In a digital universe where threats grow more sophisticated and opportunities become more exciting, Jo SNAI stands as a reminder that security should never slow innovation, it should enable it.

Welcome to the next chapter of Jo SNAI.

Same hero. New look. Stronger vision.

Security Nebula AI

Cyber Strong. AI Smart. Human First. 💜🛡️✨🚀

Microsoft Purview Adds Time-Limited Role Assignments to Strengthen Security

Microsoft is enhancing Microsoft Purview with a new capability that allows administrators to assign expiration dates to role group memberships. This update makes it easier to grant temporary administrative access while supporting the principle of least privilege, helping organizations reduce the risk associated with long-term privileged accounts.

With this new feature, administrators can specify how long a user or security group should remain in a Purview role group, choosing a duration anywhere from one day up to two years. Once the assigned period expires, access is automatically removed, helping security and compliance teams maintain tighter control over administrative permissions.

When Will It Be Available?

Microsoft plans to roll out the feature according to the following schedule:

  • Worldwide General Availability: Starting in late July 2026 and expected to complete by late August 2026.
  • GCC, GCC High, and DoD: Starting in late August 2026 and expected to complete by late September 2026.
What Does This Mean for Organizations?

This enhancement primarily benefits:

  • Microsoft Purview administrators
  • Security administrators
  • Compliance teams
  • Organizations managing role-based access through Microsoft Purview

The feature will be available through:

  • Microsoft Purview Compliance Portal
  • Microsoft Purview Role-Based Access Control (RBAC)
Key Benefits

Once the rollout is complete, administrators will be able to:

✅ Assign users or security groups to role groups with a predefined expiration date.

✅ Set assignment durations ranging from 1 day to 2 years.

✅ Apply the capability to both new and existing role assignments.

✅ Reduce the likelihood of forgotten or unnecessary privileged access.

✅ Improve governance, compliance, and security posture with minimal administrative effort.

Importantly, existing role assignments will not be automatically modified, and end-user workflows will remain unchanged.

What Do You Need to Do?

The good news is that no action is required to enable this feature. It will be available by default once deployed, with no additional configuration or policy changes needed.

However, organizations may want to take advantage of the new functionality by:

  • Reviewing privileged access management processes.
  • Using expiration-based assignments for temporary projects, audits, or administrative tasks.
  • Updating internal documentation and operational procedures.
  • Informing Purview administrators about the new capability.

From a compliance perspective, time-limited role assignments help organizations demonstrate stronger control over privileged access.

Many regulatory frameworks and security standards—including ISO 27001, NIST, SOC 2, GDPR accountability requirements, and Zero Trust security principles—expect organizations to follow the principle of least privilege, ensuring users only have access to the resources they need and only for as long as they need it.

🎙️Podcast Episode: Smarter Insider Risk Coverage with Microsoft Purview

🎙️ New podcast episode just dropped!

We’re diving into Smarter Insider Risk Coverage with Microsoft Purview together with Pip & Mara, breaking down what’s new, why it matters, and how it can help organizations stay ahead of insider risks.

If you’re working in security, compliance, or Microsoft 365, this one’s definitely worth a listen 👇

▶️ Watch now on YouTube

Stay tuned…

Smarter Insider Risk Coverage with Microsoft Purview

Microsoft is making Insider Risk Management in Purview even more useful with the introduction of a Policy Recommendation panel, a feature designed to help admins quickly spot gaps in their current risk coverage and strengthen their defenses.

Let’s face it: even with policies in place, it’s not always easy to know what you might be missing. That’s where this new capability comes in. It analyzes your existing setup and highlights missing or high-impact policies, offering clear, actionable suggestions to improve your security posture.

What’s new?

The Policy Recommendation panel lives directly on the Policies page and automatically reviews your current configuration. Using built-in analytics, it identifies areas where you could increase protection and recommends policies to cover common insider risk scenarios like:

  • Data leakage
  • Data theft
  • IP theft
  • Risky AI usage
  • Other security violations

It’s essentially a built-in advisor that helps you get more value from Insider Risk Management without needing to manually audit everything.

A quick reminder: what Insider Risk Management does

Microsoft Purview Insider Risk Management works by correlating signals across your environment to detect potentially risky behavior, whether intentional or accidental.

It’s also designed with privacy in mind, including:

  • Pseudonymization by default
  • Role-based access controls
  • Audit logs for transparency

So you can investigate risks while still protecting user privacy.

Rollout timeline
  • Public Preview: Mid–June 2026 → Late June 2026
  • General Availability: Mid–July 2026 → Late July 2026

This message is associated with Microsoft 365 Roadmap ID 560600.

Podcast Episode: DSI Investigation templates for common data security scenarios

🎙️ New podcast episode just dropped!
DSI Investigation Templates for Common Data Security Scenarios with Pip & Mara
▶️ Watch now on YouTube

Stay tuned…

Data Security Investigations: Investigation templates for common data security scenarios

Microsoft just made investigations in Purview Data Security a lot simpler and faster. You can now use ready‑made search templates designed for common data security scenarios, so you don’t have to start from scratch every time.

These built‑in templates help standardize the way investigations are run and reduce the amount of manual setup, meaning security analysts can jump straight into the work with minimal input.

The best part? This feature is already available worldwide, requires no administrative setup, and is ready to use out of the box saving valuable time and streamlining the overall investigation process.

What’s new and why it matters

Microsoft is making investigations in Purview Data Security much more approachable by introducing built‑in search templates. These templates are designed for the scenarios analysts deal with most often—like data exfiltration, compromised mailboxes, exposure of personal data, or even risky AI interactions.

Instead of building queries from scratch every time, investigators can now choose a ready‑made template, enter a few basic details (such as a user or site), and get started immediately. This not only speeds things up but also ensures investigations are more consistent across teams. It’s especially helpful for less-experienced analysts, lowering the learning curve and reducing the time needed to get value from the solution.

(This update is tracked under Microsoft 365 Roadmap ID 560326.)

Rollout timeline

  • General Availability (Worldwide): Available now

What this means for your organization

Who it impacts

  • Security analysts and investigators working with Microsoft Purview Data Security Investigations

Where you’ll see it

  • Microsoft Purview (web portal)
  • Data Security Investigations solution

In short, this update removes a lot of the friction from starting an investigation helping teams move faster, stay consistent, and focus on what actually matters: understanding and responding to risks.

Broadcast Episode: Microsoft Purview DSPM now includes a new data security agent to strengthen your data protection posture

Pip: When your data security posture needs managing, the last thing you want is to piece together risk signals manually — like assembling furniture with no instructions and half the screws missing.

Mara: Jo SNAI has a post on that exact problem — Microsoft Purview’s DSPM moving to general availability, and what the new Data Security Posture Agent actually changes for security and compliance teams. Let’s start with what that shift means in practice.

Microsoft Purview DSPM Reaches General Availability

Pip: The core question here is what changes when a security feature moves from preview to general availability — and whether GA status actually signals something meaningful for teams already managing data risk in Microsoft 365.

Mara: The post frames the value proposition directly: “Instead of piecing things together manually, you get clear insights, risk signals, and practical recommendations to help improve your overall data security posture.”

Pip: So the upshot is consolidation — one centralized view replacing a fragmented manual process, which for compliance teams managing large Microsoft 365 environments is genuinely significant.

Mara: The headline addition in this release is the Data Security Posture Agent, now fully available. It gives teams a centralized view of data risks, surfaces gaps in their security posture, and provides actionable recommendations with direct remediation steps — not just a dashboard to stare at.

Pip: The rollout window runs from late May through late June 2026, so depending on your organization’s Purview deployment timing, you may already have access or it’s arriving soon.

Mara: One detail worth flagging for teams nervous about migration headaches: the transition from preview is seamless. Existing configurations carry over intact — no policy reconfiguration required.

Pip: Which is a small but real thing. New capability with zero forced rework is not the default in enterprise security tooling.

Mara: The post identifies IT admins, security teams, and compliance professionals as the primary audience — essentially anyone responsible for data protection within Microsoft 365. And notably, no action is required to enable the feature. The recommendation is to explore the new DSPM capabilities, review how the Data Security Posture Agent fits your existing strategy, and brief your compliance teams on what’s now available.

Pip: GA status, seamless rollout, no manual toggle — the barrier to actually using this is now just knowing it exists.

Mara: Which is exactly the kind of update worth surfacing.

Pip: Visibility into data risk without rebuilding your configuration from scratch — that’s a reasonable ask, and apparently now a delivered one.

Mara: More on how these posture tools evolve in practice next time.